
Securing the SAP Transport Management System (STMS): 7 Best Practices
What is the SAP Transport Management System (STMS)?
The SAP Transport Management System (STMS) orchestrates the movement of software code, custom ABAP developments, and configuration changes across SAP environments. By controlling the lifecycle of a “transport request” from the Development system, through Quality Assurance (QA), and into Production, STMS ensures that enterprise architecture remains consistent.
While STMS functions as the primary vehicle for administrators to implement updates smoothly, it also presents unique cybersecurity challenges. Because transports deploy at multiple points in the development pipeline, malicious code or misconfigured authorizations hidden inside a transport request can easily cascade into mission-critical environments. Securing the SAP Transport Management System with dedicated DevSecOps practices is paramount to maintaining a stable and secure ERP environment.
How does SAP Transport Management Work?
SAP Transport Management governs the movement of software and configuration changes cascading across development, testing, and production environments.
A transport request packages the changes made in a development system. This request includes all required details, such as the altered objects, the SAP version, and the specific target system receiving the application updates.
Relevant stakeholders, such as developers, quality assurance personnel, and project managers, review and approve the transport request. Once approved, the request is released for migration to the target system.
The transport request migrates to the target system, where the application changes execute. The target system typically functions as a dedicated testing or production environment.
After the changes deploy, security and development teams test the configurations to ensure they function as intended and do not negatively impact other areas of the SAP ecosystem.
Once the changes achieve successful verification, administrators close the transport request to finalize the deployment cycle.
The Security Risks of SAP Transports
Integrating the SAP Transport Management System (STMS) into the software development lifecycle standardizes application deployments but creates overlooked vulnerabilities requiring specialized security oversight.
Transports deploy at multiple points in the development cycle. Because transports execute continuously throughout the development pipeline, they frequently represent a blind spot in SAP security, creating distinct opportunities for exploitation.
If a compromised development transport bypasses manual review, an attacker can leverage numerous techniques to compromise production systems through malicious transports. This exploitation directly results in the catastrophic loss of data confidentiality, system integrity, and operational availability.
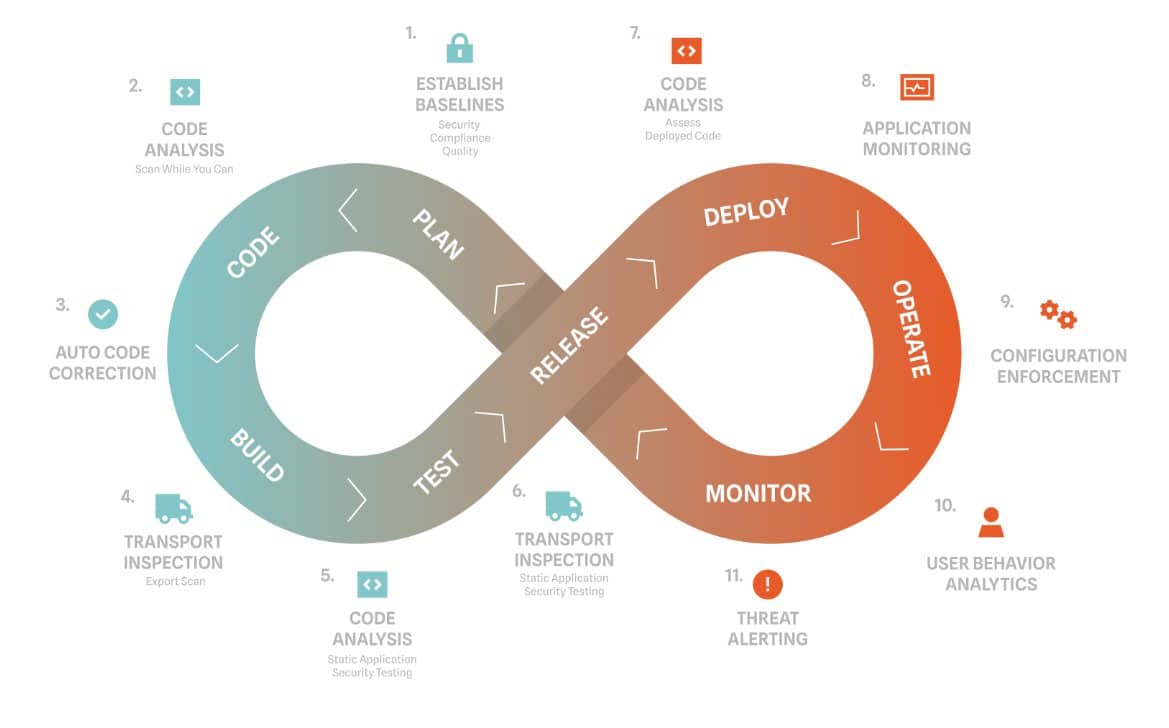
What Security Teams Should Know about SAP Transport Management
Managing enterprise systems requires balancing operational automation with rigorous risk management to mitigate specific transport vulnerabilities.
To mitigate these risks, organizations must implement strict access controls, use secure transport protocols, audit transport activities, and enforce robust segregation of duties. Additionally, implementing encryption and digital signatures can help ensure the integrity and confidentiality of transport requests.
Onapsis for SAP Transport Management
Securing the SAP backend development system holistically requires automated application security testing to inspect transports prior to production deployment.
Onapsis Control automates the monitoring of changes that are leaving the development system and provides additional approval workflows for critical situations. Control is ideal for enterprises who want to:
Ready to eliminate your SAP cyber security blindspot?
Let us show you how simple it can be to protect your business applications.