ONAPSIS DEFEND

Advanced Threat Monitoring for SAP by Defenders, for Defenders

Threat actors move fast. Catch them faster. We built Defend to bring the unmatched power of Onapsis Research Labs, the world’s leading authority on SAP threats, straight to your security operations. Get exclusive, real-time threat intelligence that detects emerging exploits and active attacks other tools miss. 

Built for Today’s AI-Driven Threats: Attackers are moving faster than ever, using AI to weaponize SAP flaws in days rather than weeks, requiring proactive machine-speed GPT enterprise threat protection. From SAP RECON (CVE-2020-6287) targeted within 72 hours of patch release to mass zero-day exploitation like CVE-2025-31324, threat actors routinely strike before defenders can apply fixes. Defend continuously tracks the evolving SAP threat landscape and turns emerging intelligence into zero-day SAP vulnerability defense, giving your team the early warning needed to investigate, respond, and intervene before an attack becomes a breach.

Ready for Tomorrow’s Agentic AI: As security becomes more automated, your AI agents will need high-fidelity threat signals they can act on. We are the only company that can provide SAP-endorsed, industry-trusted threat intelligence and act as your AI orchestration’s real-time source of truth on SAP threats. With Onapsis, your security operations and AI-driven defenses gain incredibly timely, high-confidence threat intelligence required to rapidly prioritize enterprise risk, orchestrate automated responses, and protect critical systems – whether autonomous or human-in-the-loop (HITL).
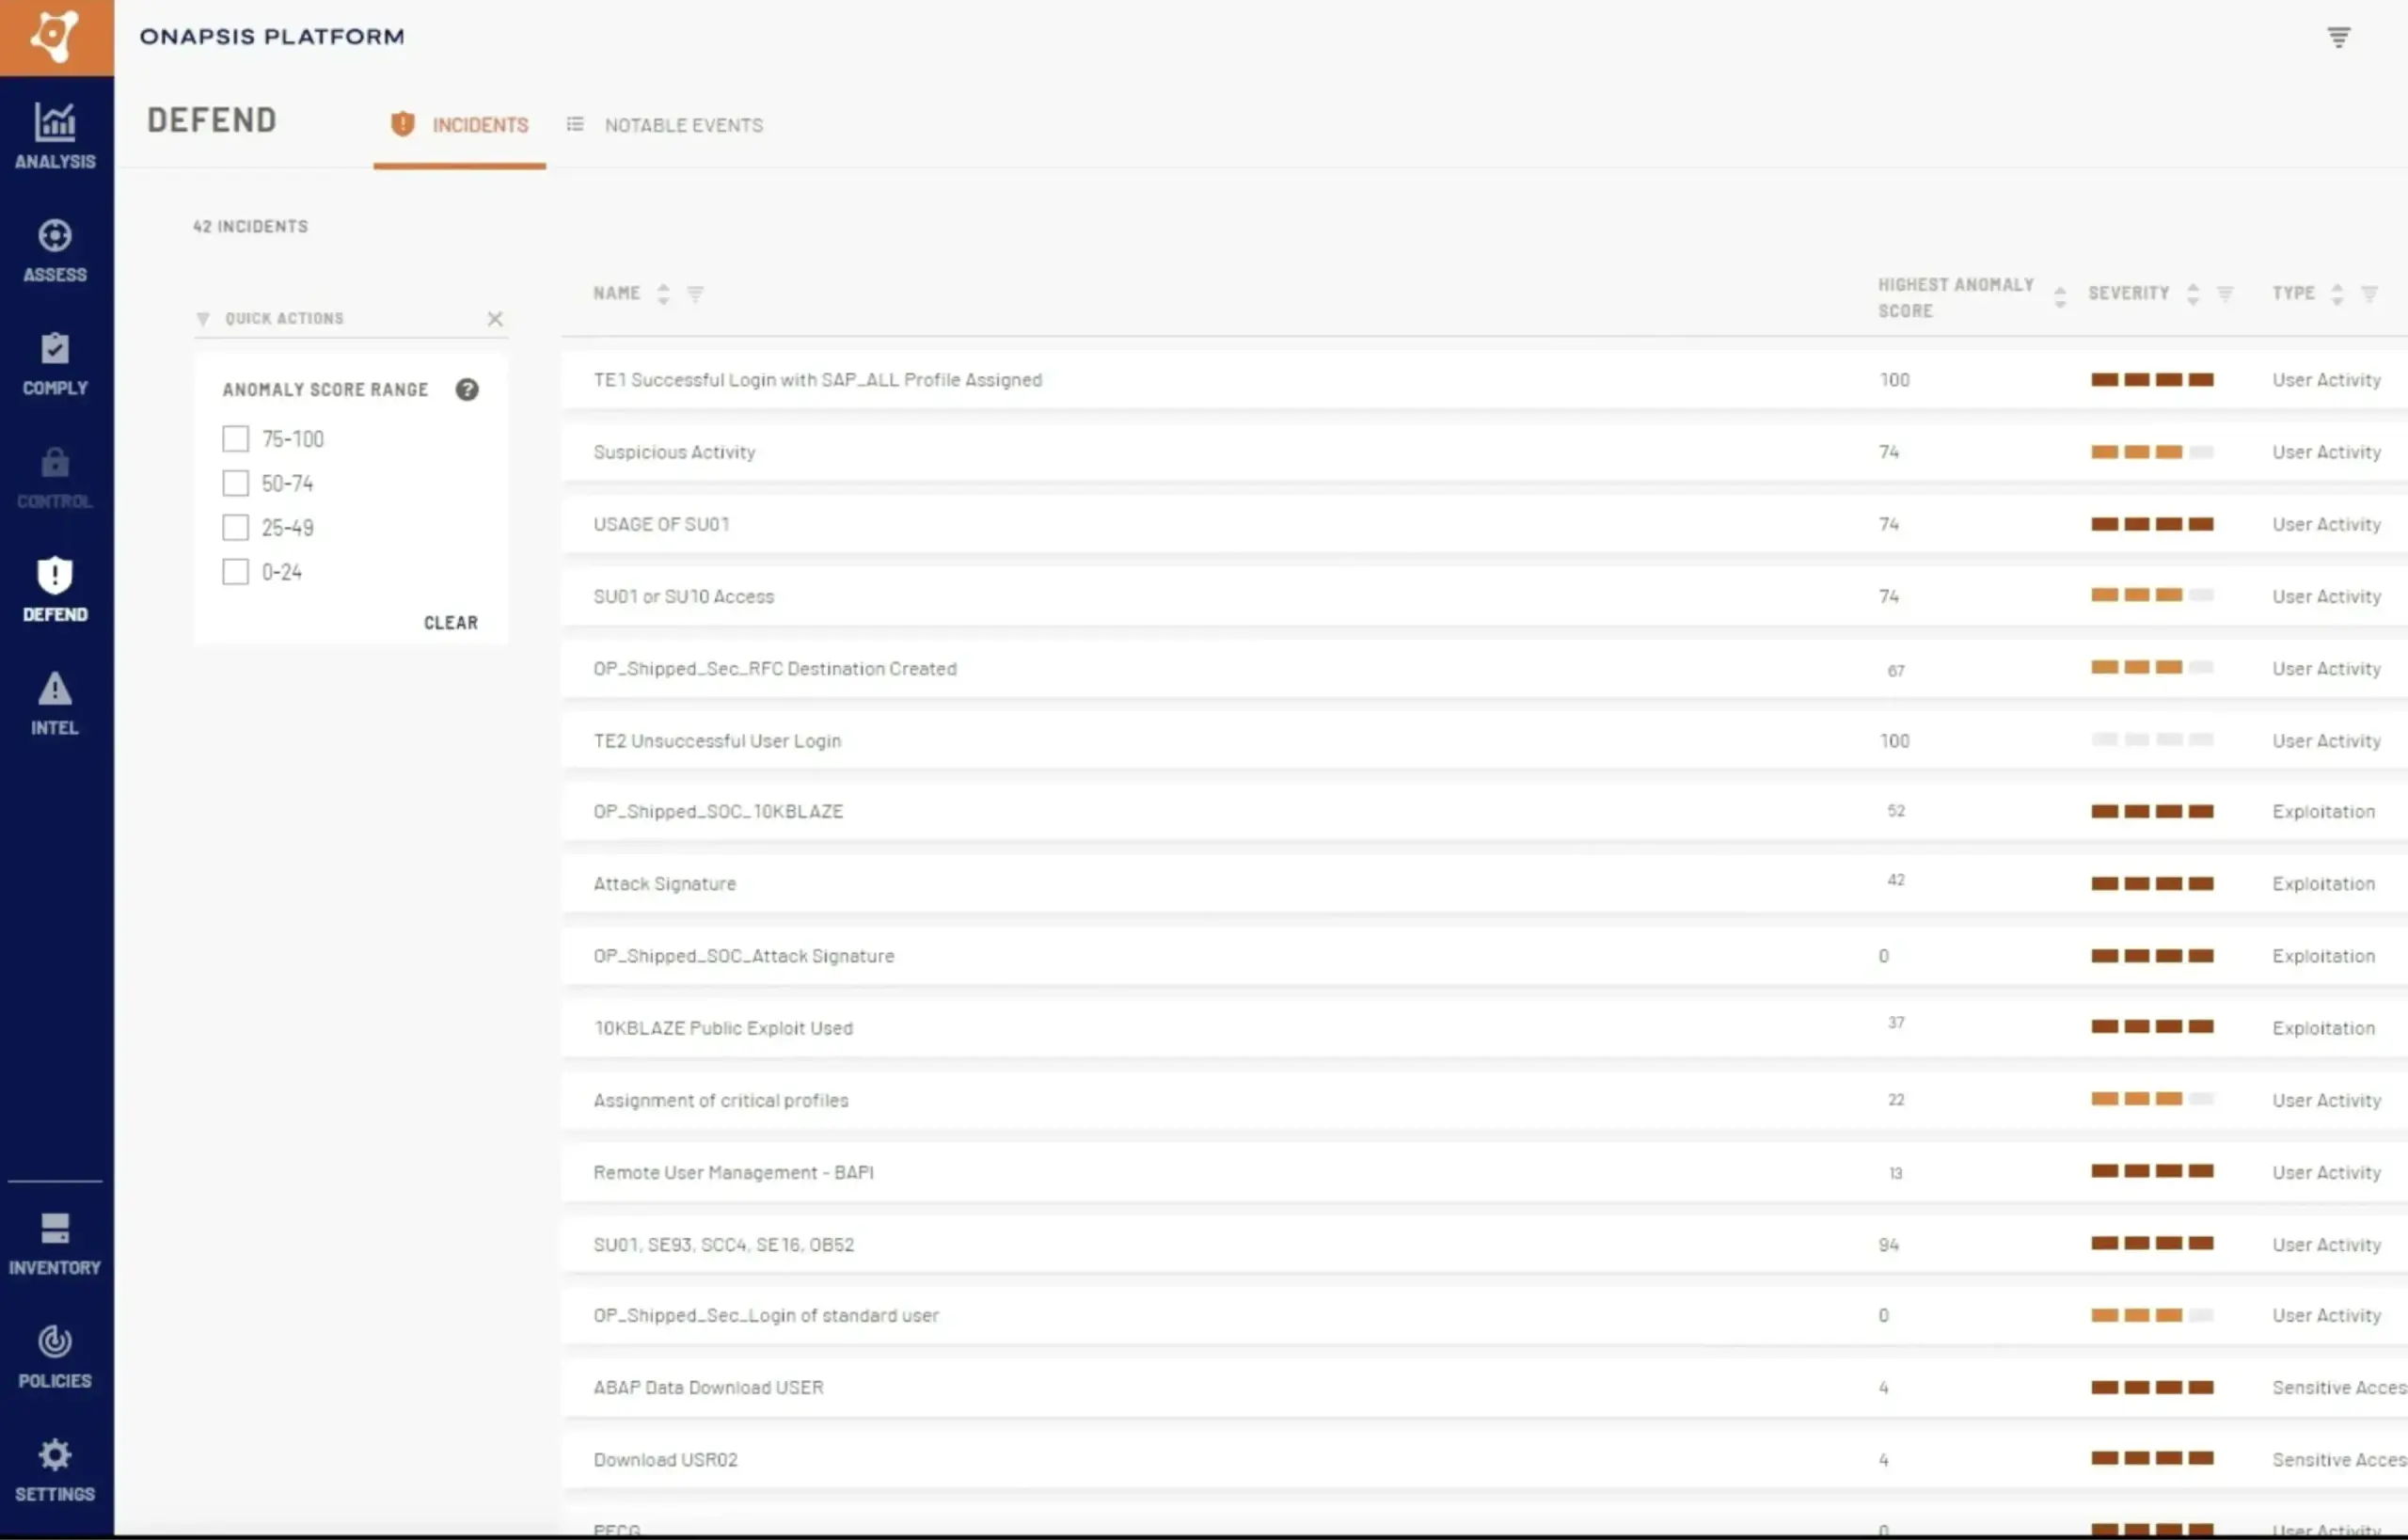
Defend Dashboard Platform image

Trusted by the worlds leading enterprises
HOW IT WORKS

Find SAP Threats Faster. Stop Them Sooner.

Step 1

Detect
SAP Threat Intelligence from the Experts

Continuously monitor your entire SAP landscape – on-prem, cloud, RISE, BTP, and more with unmatched precision. Powered by over 2,600 detection rules, Defend provides real-time SAP threat detection and response, identifying active exploits and user anomalies that other solutions miss. 

Step 2

Prioritize
Zero in on What Matters Most

Leverage the high-fidelity SAP threat intelligence from the research team credited with discovering over 1,000 zero-day vulnerabilities. By synthesizing live adversary insights with AI-powered anomaly scoring, Defend identifies and isolates high-impact threats, ensuring your team focuses exclusively on what matters most.

Step 3

Respond
Accelerate SAP Security Operations

Drive rapid incident resolution with expert guidance integrated directly with your SIEM or AI agents. Defend goes beyond standard alerts, delivering actionable mitigation insights that eliminate investigation guesswork, enabling your SOC to neutralize SAP threats in record time.

WHY DO CUSTOMERS USE ONAPSIS DEFEND?

Exclusive Threat Intelligence, Exploit Detection, & Compensating Controls to Stay Ahead of Active SAP Threats

Superior SAP Exploit Protection 

AI empowers attackers to exploit SAP vulnerabilities at scale. We track active threat groups that target SAP, like Scattered Spider, UNC5174, Storm-2460, and Qilin, providing real-time attack insights and rapid updates to our detection coverage. Leverage 600+ exclusive, proprietary exploit rules to gain unmatched, faster visibility into threats to your business and accelerate your response. 

Unparalleled SAP Zero-Day Defense

As AI dramatically accelerates vulnerability discovery, zero-days are rising rapidly. We counter this by utilizing AI to amplify the Onapsis Research Labs’ proven zero-day intelligence and expertise, providing protection an average of four months before official patches are released. Maintain a decisive advantage over the attackers targeting your business.

Continuous Protection for Unpatched Systems

Patch cycles create windows of exposure. Only Onapsis can offer robust protection during these windows. We integrate our Assess exposure management results with Defend to deploy immediate virtual patching compensating controls.  Alert on exploit activity targeting open vulnerabilities to maintain compliance with standards like NIST, ISO, NIS 2, or US SEC disclosure rules while remediation progresses. 

Elite SAP Insights for Your SOC

Unify and simplify complex SAP logs to bridge the visibility gap with InfoSec. Defend serves as your trusted, single source of truth, streaming high-fidelity threat insights and critical alerts into  your SIEM, SOAR and enterprise agentic AI orchestrations. Transform cryptic SAP application data into clear, actionable forensic insights, enabling both human analysts and autonomous workflows to triage and neutralize threats rapidly.

Support DLP: Alert on Potential Loss & Unauthorized Access

Keep a lock on your critical data beyond simple download tracking. Defend detects the precursor risks other tools miss, like over-privileged role assignments and dangerous RFC/report executions. By combining this proactive coverage with anomaly scoring and deep forensics (user, destination, anomaly score), we provide the actionable insights needed to supercharge your existing DLP workflows.

Proactively Identify Compliance Drift in Real Time

Eliminate audit surprises. Defend continuously monitors for control violations, suspicious activity, and other indicators of risk, providing real-time alerts to your team. Use our unique “alert on anything” capability to track critical risk indicators and resolve issues proactively before they impact audit outcomes.

PROVEN RESULTS

Real Impact, Measured

Hours
to the first exploit attempt on an unprotected system coming online.
Hours
between the release of an SAP patch and the first active exploit attempts in the wild.
Hours/Week Saved
compared to performing manual system log reviews.
Hours/Week Saved
addressing security controls around user access.

See Why Customers Love Onapsis Defend

Onapsis Defend Ready

Schedule a Live Demo Today

See The Power of SAP Continuous Threat Monitoring and Pre-Patch Protection

Let our technical experts show you how Onapsis Defend can keep your security team ahead of SAP system threats as well as reduce investigation times and accelerate incident response.