ONAPSIS CONTROL

Mitigate SAP Security Risks Before They Reach Production

Accelerate your AI-fueled DevSecOps strategy for SAP and shift left with automated application security testing. Empower developers to identify and remediate vulnerabilities early, ensuring secure SAP deployments without slowing down innovation.

Onapsis Control is the only SAP-endorsed automated SAP application security testing software, built on 17+ years of dedicated SAP expertise. Fueled by unmatched threat intelligence from the Onapsis Research Labs, Control natively embeds automated security across your entire pipeline. Seamlessly integrate with the SAP Business Technology Platform to secure AI- and human-generated code in Dev, at rest, and in motion. Connect your  CI/CD pipelines, Git repositories, and Cloud Transport Management to ensure secure deployments without slowing down innovation.
Trusted by the worlds leading enterprises
HOW IT WORKS

Make code security built-in, not bolted on.

Step 1

Scan

Automate Security Tests

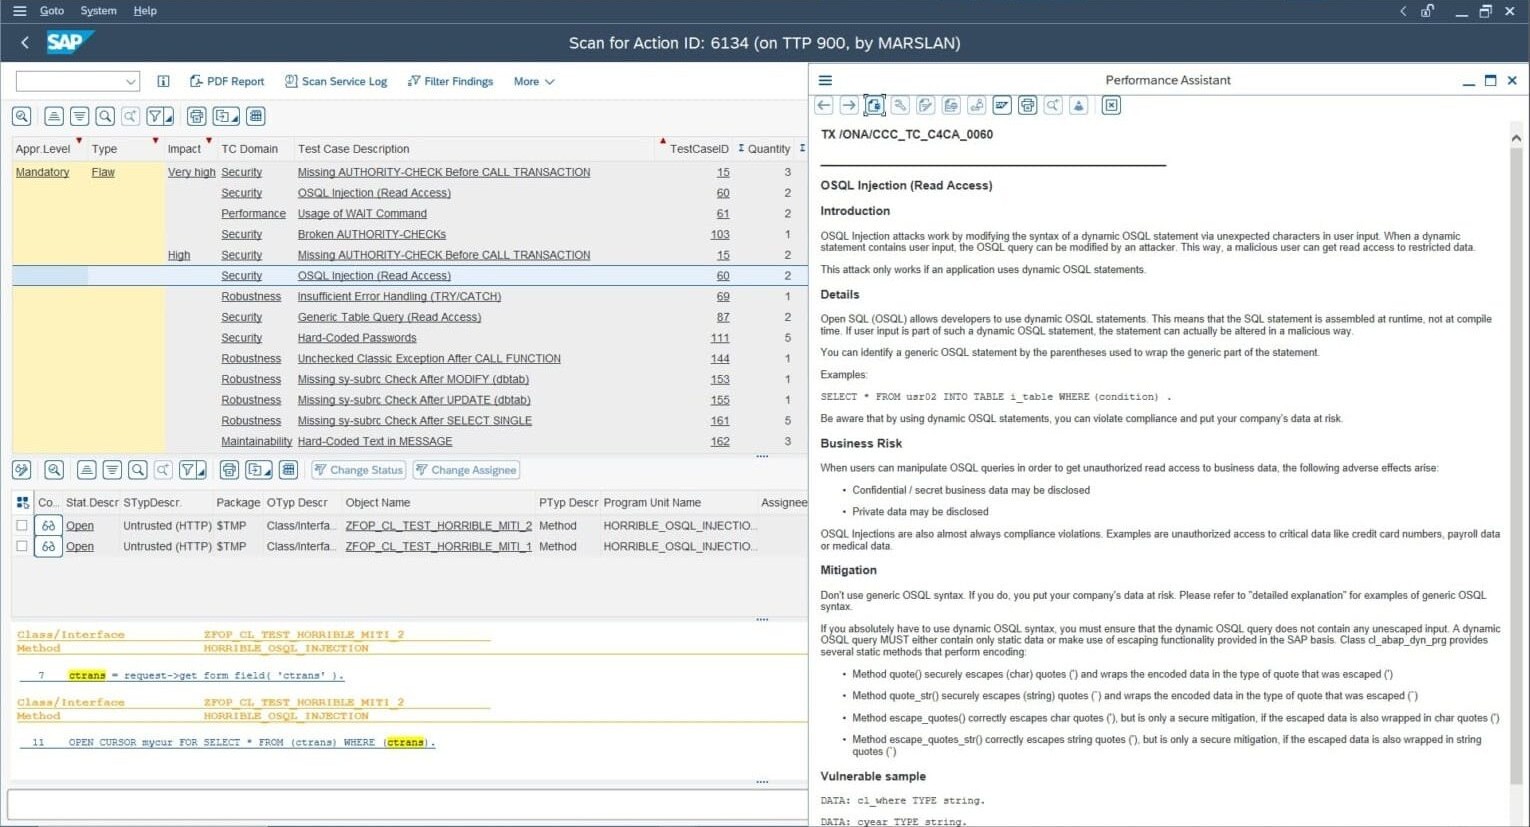
Embed automated application security testing directly into your developers’ natural workflows. Seamlessly scan custom SAP code with every commit across your IDEs, CI/CD pipelines, Git repositories, and transports to catch issues early.

Step 2

Analyze

Pinpoint Critical Code Flaws

Trust 17+ years of SAP security excellence. Fueled by Onapsis Research Labs’ threat intelligence, accurately identify vulnerabilities in your SAP custom code, minimizing false positives so developers focus on real risk.

Step 3

Remediate

Automate Fixes and Block Threats

Empower developers with automated code remediation and in-line guidance. Intercept and block vulnerable code from advancing via transports, ensuring only clean, secure applications ever reach production.

CAPABILITIES

Protect your SAP transformation and enforce your SAP secure clean core strategy

Real time IDE Scanning

Catch vulnerabilities the moment they are written in Dev. Give developers instant, “spell-check” style feedback and remediation guidance directly within their native IDEs (including Eclipse, Visual Studio Code, SAP BAS, SAP Build Code, and the classic ABAP workbench), powering automated SAP  code analysis directly at the source.

Securing AI-Generated Code

Maximize the efficiency of AI-generated code through automated vulnerability scans. Validate high volumes of code safely in just minutes instead of inaccurate and lengthy manual reviews that neutralize the speed of AI tools (e.g., from SAP Joule or SAP Build Code). Only Control delivers maximum security and the accuracy that comparable solutions and LLMs cannot reach.

Git Repository Scanning

Secure your collaborative development in Git Repositories  and hold third parties accountable. Batch-scan code at rest across GitHub, GitLab, Azure Repos, and Bitbucket. Enforce strict and consistent security with centralized policies on internal, third-party, and AI-generated code, seamlessly supporting gCTS, abapGit, and SAPUI5 before vulnerable code is ever merged.

CI/CD Pipeline Scanning

Scan every commit automatically within your existing CI/CD pipelines. Get instant feedback across Azure Pipelines, SAP Project Piper, and SAP CI/CD to block vulnerabilities early. Build a robust security layer for your SAP BTP and RISE with SAP projects while shipping faster at a lower cost.

Transport Guard

Stop risky code in motion. Control acts as an automated transport guard and quality gate to drive consistent security, scanning code while being transferred via SAP Transport Management Service (TMS) and SAP Cloud Transport Management service (cTMS). Automatically block vulnerable transports from internal and third-party teams before they reach production.

Change Management

Move projects along faster by automating security gates and approvals within your SAP DevSecOps and change management processes. On-Change Control integrates seamlessly with SAP ChaRM. This flexible framework automatically triggers scans, identifies approvers, routes emails, and documents everything in centralized logs while allowing staggered rollouts to ramp up compliance.

PROVEN RESULTS

Real Impact, Measured

Reduction in Code Review Time by Teams
Saved Annually In Code Review Costs
Saved Per System By Eliminating Import Errors
Findings seamlessly resolved
Person wearing glasses and a white shirt, illuminated by blue and purple lighting, looking at a device in a dimly lit room.

Ready to Take Control of Your ERP Security?

Discover how Onapsis Control uses rapid automated scanning to catch vulnerabilities early in your custom code—and makes remediation effortless.