Record-breaking numbers of HotNews and High Priority Notes
Navigating November’s Historic SAP Security Patch Day – LIVE WEBINAR
Join Onapsis to talk through November’s Vulnerabilities.
November 12th, 10am ET
Register here
Highlights of November SAP Security Notes analysis include:
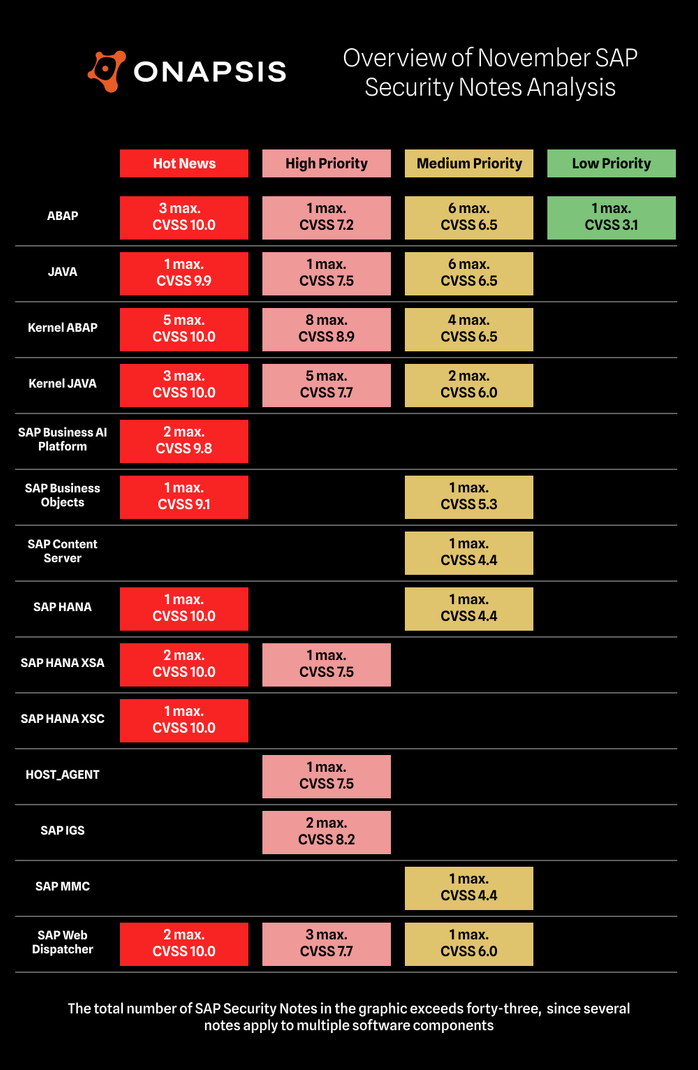
- November Summary – 43 new and updated SAP security patches released, including 12 HotNews Notes and 13 High Priority Notes
- Four CVSS 10.0 – Memory corruptions in ICM and SAP Web Dispatcher, Missing Authentication in SAP NW AS ABAP and ABAP Platform and Broken Access Control in SAP Gateway
- Onapsis Research Labs Contribution – Our team supported SAP in patching 36 vulnerabilities, covered by 24 SAP Security Notes, including 7 tagged as HotNews and 10 tagged as High Priority. 14 of the 36 Vulnerabilities, leading to 7 Security Notes were found in collaboration with XBOW.
SAP has published the record-breaking number of 43 new and updated SAP Security Notes in its November Patch Day, including 12 HotNews Notes and 13 High Priority Notes. 24 SAP Security Notes were published in collaboration with the Onapsis Research Labs.
The HotNews Notes in Detail
The Onapsis Research Labs (ORL) supported SAP in patching six of twelve HotNews Notes.
SAP Security Note #3798345, tagged with a CVSS score of 10.0, patches a Broken Access Control vulnerability in SAP Gateway. The Onapsis Research Labs (ORL) detected that an unauthenticated attacker with network access to the SAP Gateway could exploit a vulnerability in the application to potentially perform unauthorized actions within the application environment. The vulnerability is caused by the fact that SAP Gateway activates the default Access Control List with high privileges allowing categorization of external attackers as internal application servers. After implementing the SAP Security Note, customers must manually set a profile parameter to be secure. The vulnerability is tracked under CVE-2026-89103 and is dubbed PROXYGATE by the Onapsis Research Labs. More information on the PROXYGATE vulnerability can be found here
SAP Security Note #3778530, tagged with a CVSS score of 10.0, patches a Memory Corruption vulnerability in SAP NetWeaver AS ABAP (Internet Communication Manager). Our ORL team recognized that some size/length parameters in WebSocket control frames are not properly validated. This allows an unauthenticated attacker sending specially crafted network traffic to trigger a memory corruption condition in the affected functionality. Successful exploitation could allow the attacker to execute arbitrary code and fully compromise the system. As a workaround, support for WebSocket can be disabled. But since this has a significant impact on interactive and integration scenarios, it is not recommended.
SAP Security Note #3778556, tagged with a CVSS score of 10, addresses almost the same vulnerability in SAP Web Dispatcher and is also credited to the Onapsis Research Labs. In the referenced FAQ Note #3778788, SAP explains how this SAP Security Note is related to #3778530. Important: The Web Dispatcher that is part of SAP HANA Extended Application Services Classic Model and Advanced Model is also affected. SAP Content Server is not affected.
The vulnerabilities, affecting ICM and SAP Web Dispatcher, were dubbed ICM2SHELL by the Onapsis Research Labs. More information on the ICM2SHELL vulnerability can be found here
SAP Security Note #3849308, tagged with a CVSS score of 10.0, addresses a Missing Authentication vulnerability in SAP NetWeaver AS ABAP and ABAP Platform (SAML2 Service Provider). The vulnerability is caused by an insufficient verification of incoming authentication assertions under certain configurations. If not patched, unauthenticated attackers could submit specially crafted data to bypass authentication and impersonate arbitrary users, including privileged accounts. This could result in a full system compromise
The ORL team supported SAP in patching a Missing Authorization Check vulnerability in S4CRM. Certain remote-enabled function modules do not perform necessary authorization checks and lack sufficient input validation. As a result, an attacker with low privileges could send specially crafted input through a remote interface to inject and execute arbitrary code within the affected system. Successful exploitation could extend the attacker’s reach beyond the vulnerable component, resulting in a high impact on confidentiality, integrity and availability. SAP Security Note #3834842, tagged with a CVSS of 9.9, introduces appropriate authorization checks as well as code to identify and prevent any injection.
Another HotNews Note that SAP has published in collaboration with our ORL team is SAP Security Note #3792735, tagged with a CVSS score of 9.9. Researchers of the team detected certain internal functionality in SAP NetWeaver Application Server ABAP and ABAP Platform that does not perform necessary authorization checks. When acting as a low privileged attacker, they could invoke affected functionality to execute arbitrary operating system commands on the underlying host. Successful exploitation could impact resources beyond the vulnerable component, resulting in a high impact on confidentiality, integrity and availability of the system.
The ORL team, in collaboration with XBOW, also supported SAP in patching a CVSS 9.9 Code Injection vulnerability in SAP NetWeaver Knowledge Management (XML Forms). Under certain conditions, an authenticated user with access to the vulnerable functionality could cause an unauthorized XSL transformation to be processed, potentially leading to arbitrary code execution in the application context. The vulnerability is patched with SAP Security Note #3809153 by restricting request-selected XSL transformations to only those explicitly configured for the current XML Forms project. Any unconfigured or unresolved transformation identifiers are now rejected.
SAP Security Note #3805589, tagged with a CVSS score of 9.9, was initially released on SAP’s October patch day and patches a critical Code Injection vulnerability in SAP S/4HANA (Manage Substitution/Validation Rules). The updated note contains additional correction instructions for S4CORE 105 and 106.
Two HotNews Notes affect SAP Business AI Platform and were published by SAP between October and November patch day:
SAP Security Note #3843368, tagged with a CVSS score of 9.8 was initially released on October 28 and patches a Memory Corruption vulnerability in Node.js Brotli decoder. The vulnerability allows an attacker to leverage an error-handling flaw in the Brotli decoder’s block-switch processing. Under certain conditions, this can cause memory corruption (out-of-bounds write) leading to high impact on confidentiality, integrity and availability. The note comes with detailed solution descriptions for SAP BTP, Cloud Foundry and Kyma Runtime and other Brotli consumers.
SAP Security Note #3846599, tagged with a CVSS score of 9.8, patches two Remote Code Execution vulnerabilities (CVE-2026-109618, CVE-2026-109619) in SAP Business AI Platform, which are collectively known as the php2shell Remote Code Execution (RCE) chain. Both vulnerabilities are network-exploitable, require no privileges and no user interaction, and affect all active PHP 8.x minor lines (8.2.x, 8.3.x, 8.4.x, 8.5.x). They can be chained together in a combined attack vector, where the memory corruption condition established by CVE-2026-109618 could be further exploited. The note comes with detailed solution descriptions for SAP BTP, Cloud Foundry and Kyma Runtime.
SAP Security Note #3804858, tagged with a CVSS score of 9.6, patches two Cross-Site Request Forgery (CSRF) vulnerabilities in SAP Web Dispatcher and Internet Communication Manager (ICM) as well as in SAP HANA XSA Web Dispatcher. The vulnerabilities were reported by the ORL team after detecting that they allow unauthenticated attackers to trick a logged-on administrator into visiting a malicious link. Visiting the link could cause unintended actions in the administrator’s session. While the vulnerability in SAP Web Dispatcher and ICM could lead to a full system compromise, SAP HANA XSA Web Dispatcher can only be compromised temporarily, with high impact on confidentiality, but only partial impact on integrity, and availability.
SAP Security Note #3799117, tagged with a CVSS score of 9.1, patches an XML External Entity (XXE) Vulnerability in SAP BusinessObjects Business Intelligence Platform (Web Intelligence). The application does not properly restrict external entity resolution when processing OLAP connection requests. An authenticated attacker could exploit this vulnerability to access restricted resources, enabling them to read sensitive files on the server and reach internal systems that are not otherwise exposed, impacting resources beyond the vulnerable component, resulting in a high impact on confidentiality and a low impact on both integrity and availability.
The High Priority Notes in Detail
The Onapsis Research Labs (ORL) supported SAP in patching ten of thirteen High Priority Notes.
| SAP Note | CVSS | Description |
| 3809953 | 8.2 | [CVE-2026-120008] Memory Corruption Vulnerability in SAP NetWeaver (Internet Graphics Service) |
| 3803832 | 7.7 | [CVE-2026-109800] Memory Corruption vulnerability in SAP Web Dispatcher |
| 3789273 | 7.5 | [CVE-2026-76973] Memory Corruption vulnerability in Application Server ABAP of SAP NetWeaver and ABAP Platform (SAP Message Server) |
| 3792915 | 7.5 | [CVE-2026-76970] Memory Corruption vulnerability in Application Server ABAP for SAP NetWeaver and ABAP Platform |
| 3805570 | 7.5 | [CVE-2026-120010] Memory Corruption vulnerability in SAP NetWeaver Application Server (SAP Message Server) |
| 3805681 | 7.5 | [CVE-2026-109794] Denial of Service vulnerability in SAP NetWeaver Application Server ABAP, ABAP Platform and SAP Web Dispatcher |
| 3808627 | 7.5 | [CVE-2026-109793] Denial of Service (DoS) vulnerability in SAP NetWeaver Application Server ABAP (Internet Communication Manager) and SAP Web Dispatcher |
| 3809934 | 7.5 | [Multiple CVEs] Multiple Vulnerabilities in SAP NetWeaver (Internet Graphics Service) |
| 3810485 * | 7.5 | [CVE-2026-89114] Missing Authentication check in SAP NetWeaver AS Java EDM Application |
| 3842766 | 7.5 | [CVE-2026-120015] Insufficient Input Validation in SAP Host Agent |
* SAP Security Note 3810485 was identified in collaboration with XBOW.
Another High Priority vulnerability that was patched in collaboration with SAP is tracked under CVE-2026-120014 and is included in HotNews Note #3804858.
Further High Priority Notes
SAP Security Note #3769130, tagged with a CVSS score of 8.9, patches multiple vulnerabilities in Application Server ABAP of SAP NetWeaver and ABAP Platform.
Due to improper RFC protocol validation in the SAP Kernel used by the Application Server ABAP of SAP NetWeaver and ABAP Platform, an unauthenticated attacker can send a crafted RFC request that exploits logical errors in memory management, leading to memory corruption (CVE-2026-76966).
SAP NetWeaver Application Server ABAP and ABAP Platform does not properly initialize memory in certain internal components. Under certain conditions, an attacker with low privileges could disclose uninitialized memory contents under specific conditions (CVE-2026-109796).
SAP Security Note #3808552, tagged with a CVSS score of 7.5, addresses an Information Disclosure vulnerability in SAP NetWeaver (SAP Message Server). Improper handling of certain malformed requests could be leveraged by an unauthenticated attacker to send specially crafted input. Successful exploitation could allow the attacker to retrieve sensitive information, resulting in a high impact on confidentiality.
SAP Security Note #3833364, tagged with a CVSS score of 7.2, patches a Code Injection vulnerability in SAP ABAP Developer Tools (AMDP Data Preview). The application does not perform sufficient validation and authorization checks within certain affected functionality. An attacker with high privileges could submit specially crafted input to inject and execute arbitrary code on the system. Successful exploitation could allow the attacker to fully compromise the system.
Onapsis Contribution
The Onapsis Research Labs (ORL) contributed significantly to SAP’s November Patch Day. In addition to six HotNews Notes and ten High Priority Note, the ORL supported SAP in patching eight additional SAP Security Notes:
| SAP Note | CVSS | Description |
| 3805959 | 6.5 | [CVE-2026-89131] Cross Site Request Forgery (CSRF) vulnerability in SAP NetWeaver Enterprise Portal |
| 3839977 * | 6.5 | [CVE-2026-89131] Cross Site Request Forgery (CSRF) vulnerability in SAP NetWeaver Enterprise Portal |
| 3786876 | 6.4 | [CVE-2026-89131] Cross Site Request Forgery (CSRF) vulnerability in SAP NetWeaver Enterprise Portal |
| 3797108 * | 6.1 | [CVE-2026-89131] Cross Site Request Forgery (CSRF) vulnerability in SAP NetWeaver Enterprise Portal |
| 3806484 | 6.1 | [CVE-2026-89131] Cross Site Request Forgery (CSRF) vulnerability in SAP NetWeaver Enterprise Portal |
| 3835738 * | 5.8 | [CVE-2026-89131] Cross Site Request Forgery (CSRF) vulnerability in SAP NetWeaver Enterprise Portal |
| 3792447 * | 5.3 | [CVE-2026-89131] Cross Site Request Forgery (CSRF) vulnerability in SAP NetWeaver Enterprise Portal |
| 3801587 * | 4.3 | [CVE-2026-89131] Cross Site Request Forgery (CSRF) vulnerability in SAP NetWeaver Enterprise Portal |
* SAP Security Notes 3839977,3797108,3835738, 3792447 and 3801587 were identified in collaboration with XBOW.
Summary & Conclusions
SAP’s November Patch Day has broken several records. With forty-three new and updated SAP Security Notes, including twelve HotNews and thirteen High Priority Notes, SAP administrators will be very busy this week. It was also a record-holding patch day for the Onapsis Research Labs. We could support SAP in patching thirty-six vulnerabilities, covered by twenty-four SAP Security Notes, including seven tagged as HotNews and ten tagged as High Priority Notes.
| SAP Note | Type | Description | Priority | CVSS |
| 3849308 | New | [CVE-2026-120017] Missing Authentication in SAP NetWeaver AS ABAP and ABAP Platform (SAML2 Service Provider) BC-SEC-LGN-SML | HotNews | 10 |
| 3798345 | New | [CVE-2026-89103] Broken Access Control in SAP Gateway BC-CST-GW | HotNews | 10 |
| 3778556 | New | [CVE-2026-89126] Memory Corruption vulnerability in SAP Web Dispatcher BC-CST-WDP | HotNews | 10 |
| 3778530 | New | [CVE-2026-76964] Memory Corruption Vulnerability in SAP NetWeaver AS ABAP (Internet Communication Manager) BC-CST-IC | HotNews | 10 |
| 3834842 | Update | [CVE-2026-109795] Missing authorization check in S4CRM CRM-BF-SVY | HotNews | 9.9 |
| 3809153 | New | [CVE-2026-109803] Code Injection vulnerability in SAP NetWeaver Knowledge Management (XML Forms) EP-KM-CM | HotNews | 9.9 |
| 3792735 | New | [CVE-2026-76965] OS Command Injection vulnerability in ABAP Application Server for SAP NetWeaver and ABAP Platform BC-SRV-COM-FTP | HotNews | 9.9 |
| 3805589 | Update | [CVE-2026-89107] Code Injection vulnerability in SAP S/4HANA (Manage Substitution/Validation Rules) FI-SL-VSR | HotNews | 9.9 |
| 3846599 | New | [Multiple CVEs] Remote Code Execution vulnerability in PHP affecting SAP Business AI Platform BC-CP-CF-BLDP | HotNews | 9.8 |
| 3843368 | New | [CVE-2026-111497] Memory Corruption in Node.js Brotli decoder affecting SAP Business AI Platform BC-CP-SEC-VUL | HotNews | 9.8 |
| 3804858 | New | [CVE-2026-89119] Cross-Site Request Forgery (CSRF) vulnerability in SAP Web Dispatcher and Internet Communication Manager BC-CST-WDP | HotNews | 9.6 |
| 3799117 | New | [CVE-2026-109798] XML External Entity (XXE) Vulnerability in SAP BusinessObjects Business Intelligence Platform (Web Intelligence) BI-BIP-SL | HotNews | 9.1 |
| 3769130 | New | [CVE-2026-76966] Multiple vulnerabilities in Application Server ABAP of SAP NetWeaver and ABAP Platform BC-MID-RFC | High | 8.9 |
| 3809953 | New | [CVE-2026-120008] Memory Corruption Vulnerability in SAP NetWeaver (Internet Graphics Service) BC-FES-IGS | High | 8.2 |
| 3803832 | New | [CVE-2026-109800] Memory Corruption vulnerability in SAP Web Dispatcher BC-CST-WDP | High | 7.7 |
| 3789273 | New | [CVE-2026-76973] Memory Corruption vulnerability in Application Server ABAP of SAP NetWeaver and ABAP Platform (SAP Message Server) BC-CST-MS | High | 7.5 |
| 3792915 | New | [CVE-2026-76970] Memory Corruption vulnerability in Application Server ABAP for SAP NetWeaver and ABAP Platform BC-ABA-SC | High | 7.5 |
| 3842766 | New | [CVE-2026-120015] Insufficient Input Validation in SAP Host Agent BC-CCM-HAG | High | 7.5 |
| 3810485 | New | [CVE-2026-89114] Missing Authentication check in SAP NetWeaver AS Java EDM Application BC-DWB-JAV-J2E | High | 7.5 |
| 3809934 | New | [Multiple CVEs] Multiple Vulnerabilities in SAP NetWeaver (Internet Graphics Service) BC-FES-IGS | High | 7.5 |
| 3808627 | New | [CVE-2026-109793] Denial of Service (DoS) vulnerability in SAP NetWeaver Application Server ABAP (Internet Communication Manager) and SAP Web Dispatcher BC-CST-DP | High | 7.5 |
| 3808552 | New | [CVE-2026-109804] Information Disclosure in SAP NetWeaver (SAP Message Server) BC-CST-MS | High | 7.5 |
| 3805681 | New | [CVE-2026-109794] Denial of Service vulnerability in SAP NetWeaver Application Server ABAP, ABAP Platform and SAP Web Dispatcher BC-CST-IC | High | 7.5 |
| 3805570 | New | [CVE-2026-120010] Memory Corruption vulnerability in SAP NetWeaver Application Server (SAP Message Server) BC-CST-MS | High | 7.5 |
| 3833364 | New | [CVE-2026-120009] Code Injection vulnerability in SAP ABAP Developer Tools (AMDP Data Preview) BC-DWB-AIE-DP | High | 7.2 |
| 3805959 | New | [CVE-2026-109811] Server-Side Request Forgery (SSRF) vulnerability in SAP NetWeaver and ABAP Platform (Application Server ABAP) BC-MID-ICF | Medium | 6.5 |
| 3839977 | New | [Multiple CVEs] Security Vulnerabilities SAP NetWeaver Application Server Java (NWDI Cockpit) BC-CTS-DI | Medium | 6.5 |
| 3793716 | New | [CVE-2026-109802] Denial of Service (DoS) vulnerability in SAP NetWeaver Application Server for ABAP BC-MID-RFC | Medium | 6.5 |
| 3756450 | Update | [CVE-2026-44766] – SQL Injection vulnerability in SAP S/4HANA (Intercompany Matching and Reconciliation) FIN-CS-ICR | Medium | 6.5 |
| 3786876 | New | [CVE-2026-109805] Weak Cryptography in SAP NetWeaver and ABAP Platform (Application Server ABAP) BC-MID-RFC | Medium | 6.4 |
| 3703856 | Update | [CVE-2026-24309] Missing Authorization check in SAP NetWeaver Application Server for ABAP BC-DB-ORA-CCM | Medium | 6.4 |
| 3806484 | New | [CVE-2026-120016] Cross-Site Scripting (XSS) vulnerability in SAP NetWeaver Visual Composer EP-VC-RTM | Medium | 6.1 |
| 3797108 | New | [CVE-2026-109810] CSS Injection vulnerability in SAP NetWeaver Application Server Java (Web Dynpro Java) BC-WD-JAV | Medium | 6.1 |
| 3782056 | New | [CVE-2026-89125] Insecure Storage of Sensitive Information in SAP Web Dispatcher and Internet Communication Manager BC-CST-WDP | Medium | 6 |
| 3835738 | Update | [CVE-2026-89129] Server-Side Request Forgery in SAP NetWeaver AS Java (Web Services) BC-JAS-SEC-WSS | Medium | 5.8 |
| 3671819 | Update | [CVE-2026-76976] Cross-Site Scripting (XSS) vulnerability in SAP NetWeaver Application Server ABAP (Applications based on SAP GUI for HTML) BC-FES-CTL | Medium | 5.4 |
| 3792447 | New | [CVE-2026-89128] Broken Access Control in SAP NetWeaver Process Integration (Process Integration Test Tool) BC-XI-PIT | Medium | 5.3 |
| 3803144 | New | [CVE-2026-73635] Denial of service (DoS) in SAP Business Objects BI-BIP-CMC | Medium | 5.3 |
| 3740168 | New | [CVE-2026-89115] Information Disclosure vulnerability in SAP Start Service and SAP Microsoft Management Console BC-CST-STS | Medium | 4.4 |
| 3801587 | New | [CVE-2026-89131] Cross Site Request Forgery (CSRF) vulnerability in SAP NetWeaver Enterprise Portal EP-PIN-NAV | Medium | 4.3 |
| 3101986 | Update | Prepare CSP support for On-Premise down port for code dependency in SAP WebClient UI CA-WUI-UI | Medium | 4.1 |
| 3155685 | Update | [CVE-2026-44768] Security misconfiguration in SAP WebClient UI CA-WUI-UI | Medium | 4.1 |
| 3802244 | New | [CVE-2026-109808] Missing Authorisation Check in SAP Solution Tools Plug-In (ST-PI) SV-SMG-SDD | Low | 3.1 |
As always, the Onapsis Research Labs is already updating The Onapsis Platform to incorporate the newly published vulnerabilities into the product so that our customers can protect their businesses.
For more information about the latest SAP security issues and our continuous efforts to share knowledge with the security community, subscribe to our monthly Defender’s Monthly Newsletter.