
Why Secure SAP AI and RISE Now?
Record-breaking zero-days, a 400% surge in ransomware, and AI-accelerated exploits mean the traditional approach to SAP security is obsolete. Moving to RISE with SAP secures your infrastructure, but you still own the application layer. Uncover the new rules of the shared responsibility model and see why global enterprises partner with Onapsis to protect their business-critical applications from the next wave of sophisticated attacks.
Trusted by the worlds leading enterprises
The New Threat Landscape: SAP is Now a Prime Target
Threat actors have always targeted business-critical SAP applications. However, the rapid migration of SAP applications to the cloud over the last few years has had the unintended consequence of providing adversaries with more opportunities to compromise unprotected SAP systems directly. This has resulted in a record acceleration of threat actors focused and able to exploit SAP applications, increasing the frequency and sophistication of cyberattacks against SAP systems.
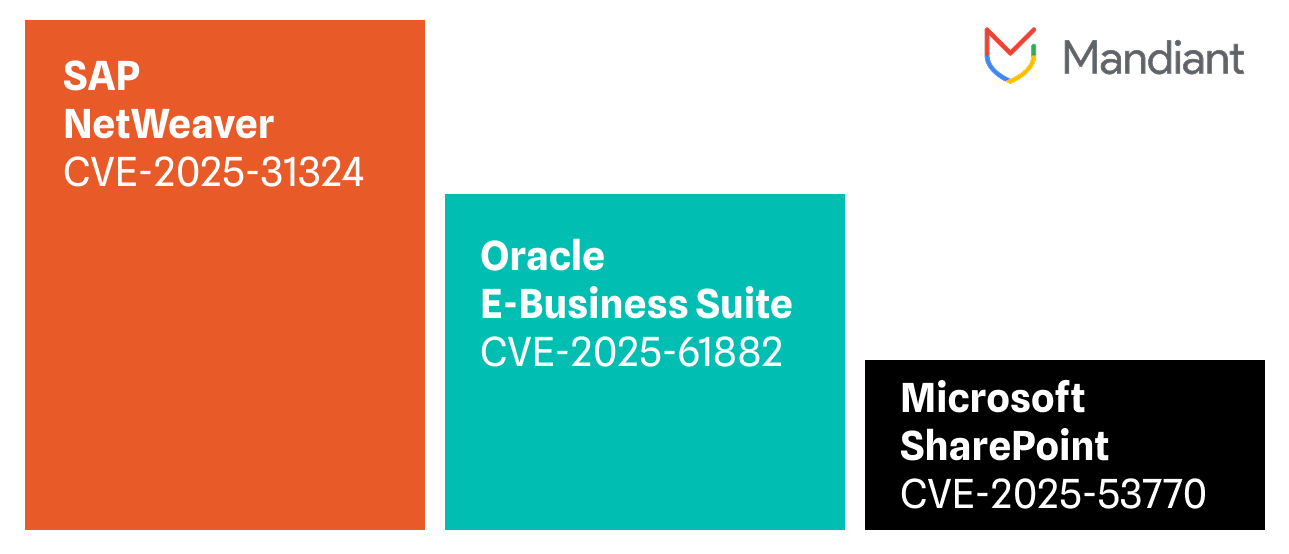
The most exploited vulnerability according to Mandiant? An SAP Zero-Day. 2025 was a critical inflection point for SAP adversarial behavior with more high severity vulnerabilities and attacks than ever before, including the SAP NetWeaver Visual Composer zero day (CVE-2025-31324). Mandiant’s M-Trends 2026 report highlighted this as the most frequently-exploited vulnerability in 2025. Waves upon waves of attack campaigns battered SAP defenders and caused billions of dollars in damages. Protecting SAP has now become a critical prioritiy for leading CISOs and CIOs. .
Most Frequently Exploited Vulnerabilities
AI Now Creates The Perfect Storm for SAP Security
With the backdrop of SAP threat activity hitting a record-high in 2025, AI revolutionized the cybersecurity world by introducing unparalleled new capabilities to both adversaries and defenders. Today, SAP Defenders face the quadruple challenge of protecting against:
Rapid increase in new SAP zero-day vulnerabilities and attacks, for which SAP patches would not be available
Exploits being derived from SAP security patches in minutes, not days/weeks, significantly increasing risk until patch implementation
Higher frequency and speed of sophisticated SAP attacks, as AI automates attack lifecycle and upskills median threat actors with SAP attack techniques, tools and procedures.
Influx of vulnerabilities in AI-generated SAP custom code in BTP and ABAP environments.
It’s enough to overwhelm any team, which is why global enterprises partner with Onapsis and the Onapsis Research Labs to deliver trusted high-fidelity threat insights, guidance, and technology capable of defending their SAP landscapes against the collective cybersecurity challenges of AI.
<72 hours
Rapid SAP Patch Weaponization: It takes threat actors less than 72 hours to exploit newly released SAP Security Notes, and this time continues to shrink rapidly.
400%
SAP Ransomware Escalation: Onapsis Research Labs have observed a 400% increase in ransomware attacks targeting SAP applications over the last three years as more sophisticated, well-funded threat actor groups turn their attention to SAP.
490%
Dark Web Activity: There has been a 490% increase in dark web criminal conversations focused on monetizing SAP exploits and vulnerabilities.
You Still Own Security in RISE with SAP. Onapsis is the SAP-Endorsed Solution that Solves This
One of the biggest misconceptions when enterprises migrate to RISE with SAP is that all security is 100% offloaded to SAP. That’s simply not true. While SAP delivers a highly secure cloud infrastructure in RISE, the customer remains fully accountable and responsible for what goes into the cloud.
Scroll horizontally to compare responsibilities.
| Security Domain | SAP’s Responsibility | Customer’s Responsibility (Your Role) |
|---|---|---|
| Infrastructure (IaaS) | Manages the hyperscaler relationship and infrastructure. | N/A |
| OS & DB Patching | Applies technical patches to the OS and standard database. | N/A |
| Application Patching (Security Notes) | Applies some critical patches as part of the managed service. | Must assess, request, and validate ALL application-level patches. |
| Application Configuration | Provides the default, “vanilla” system. | 100% RESPONSIBLE for all secure configuration and system hardening. |
| Identity & Access (Roles, SoD) | Provides the default user/role tools. | 100% RESPONSIBLE for all user provisioning, role creation, and SoD management. |
| Custom Code (ABAP/BTP) | N/A | 100% RESPONSIBLE for the security, compliance, and performance of all custom code. |
| Integrations (APIs, RFCs) | Secures its own platform endpoints. | 100% RESPONSIBLE for securing all third-party integrations, APIs, and RFC connections. |
| Data Security & Classification | N/A | 100% RESPONSIBLE for classifying and protecting all business and user data. |
| Application Threat Monitoring | Monitors its own infrastructure. | 100% RESPONSIBLE for monitoring the application layer for suspicious user behavior and vulnerability exploitation |
| Audit & Compliance | Provides infrastructure-level audit reports (e.g., SOC 2). | 100% RESPONSIBLE for all application-level audit evidence and controls for SOX, GDPR, NIS2, DORA, HIPPA and others. |
| Incident Response and Investigation | Responsible for IR on infrastructure-level attacks. | 100% RESPONSIBLE for all application-level incident investigation and remediation (unauthorized user activity, vulnerability exploitation, etc). |
While customers can outsource certain partial operations in the shared security model that they normally own to SAP Cloud Application Services (CAS) for an annual managed services fee, RISE customers can’t outsource everything (e.g., “were Security Notes applied completely and correctly?”). At the end of the day, the responsibility and accountability for security and compliance remains yours.
This is why both SAP and leading global enterprises trust Onapsis, the only SAP-endorsed solution for RISE application security, and partner with us for achieving complete security in RISE with SAP deployments.
“Together, SAP and Onapsis provide enhanced security for RISE with SAP. SAP delivers a highly-secure and compliant RISE with SAP cloud infrastructure, enabling customers to focus solely on securing their SAP applications and data.
Onapsis strategically complements SAP’s role, delivering the essential security and compliance capabilities customers need to achieve this.”
– Roland Costea (former CISO, SAP ECS / RISE with SAP)